Blog
- Business processes
- Business transformation
- Careers
- Change management
- Communication
- Company culture
- Corporate governance
- Diversity
- Enterprise architecture
- Hr alignment & leadership
- Interim management
- Leadership
- Management
- Motivation
- Personal coaching
- Problem solving
- Project management
- Strategy and positioning
- Stress management
- Team effectiveness
- Information security
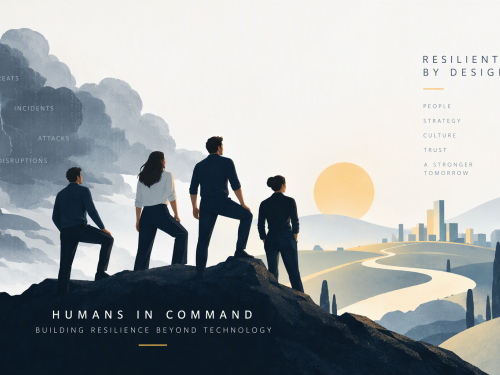
Humans in Command: Building Resilience Beyond Technology
Reflections from BE-CYBER 2026 on sovereignty, resilience and our increasingly interconnected world – part 1
From Risk to Opportunity: The Other Side of the Coin
Every risk hides an opportunity. ISO 27001 doesn't just ask what could go wrong. It asks what could go better. The difference isn't in the data. It's in the perspective.
Most companies are already managing information security risk. Just not on purpose.
Most businesses are managing risks in information security by defaulting to one option. ISO 31000 defines 4 ways to respond. Knowing the difference could save your business. Start by asking: how big is the risk you're carrying?